#wazza

2 posts · Last used Sep 24

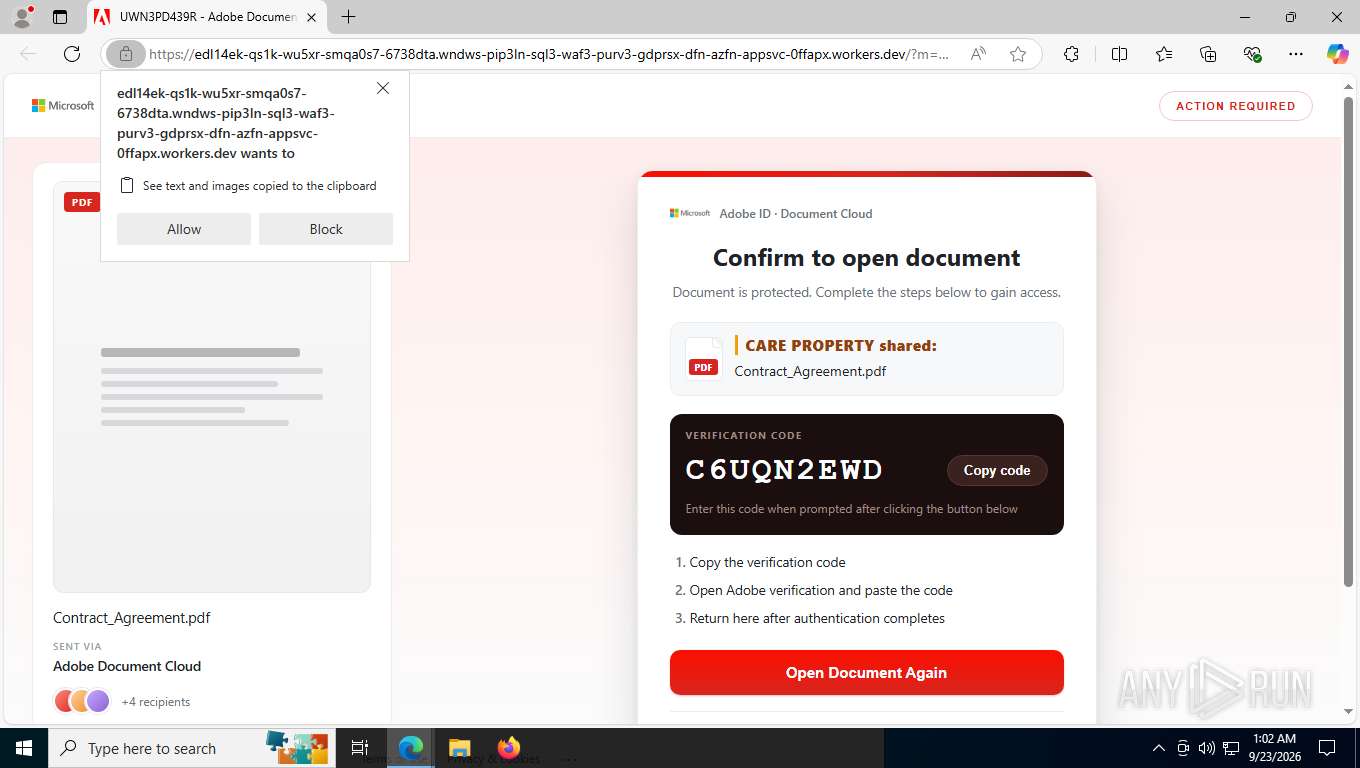
🚨 We identified #Wazza, a new phishkit targeting banking, manufacturing, and government orgs in the US, Europe, and Australia. It evades automated detection by routing victims through campaign checks and anti-bot filters before sending them to an Adobe-themed Device Code #phishing page. See each stage unfold in #ANYRUN Sandbox and gather #IOCs: https://app.any.run/tasks/be1f83a0-742a-42de-afe4-c20110ef667f/?utm_source=mastodon&utm_medium=post&utm_campaign=wazza_phishkit&utm_term=230926&utm_content=linktoservice#cybersecurity #infosec
0
1
0
0
Replying to
🚨 #Wazza phishkit routing flow: 1️⃣ *[.]boegl-krysl[.]eu — unique wildcard landing. 2️⃣ /api/wazza-config — checks whether the hostname belongs to an active campaign. 3️⃣ beacon-surge-sync[...]workers[.]dev — issues a client marker to correlate the visit. 4️⃣ /api/mint-token — creates a short-lived signed session token. 5️⃣ check[.]boegl-krysl[.]eu — validates the token and browser telemetry, filters unwanted traffic. 6️⃣ boegl-krysl[.]eu/r ➡️️ /meline — after the anti-bot check, the victim is sent through two intermediate redirect endpoints to the final Adobe-themed Device Code phishing landing page. 🔍 Pivot from #IOCs and subscribe to query updates to proactively track evolving activity:
0
1
0
0