#patchnow
26 posts · Last used Sep 29
Four Apache Karaf vulnerabilities, including CVE-2026-92142, let viewer and manager users reach admin or RCE. Upgrade to Karaf 4.4.12 now.
#ApacheKaraf #KarafVulnerabilities #Apache #PrivilegeEscalation #RCE #JMX #JavaSecurity #PatchNow
wolfSSL 5.9.4 patches 10 wolfSSL vulnerabilities, including TLS authentication bypass flaws CVE-2026-93302 and CVE-2026-89136. Upgrade now.
#wolfSSL #wolfSSLVulnerabilities #TLS #AuthenticationBypass #EmbeddedSecurity #Cryptography #IoTSecurity #PatchNow
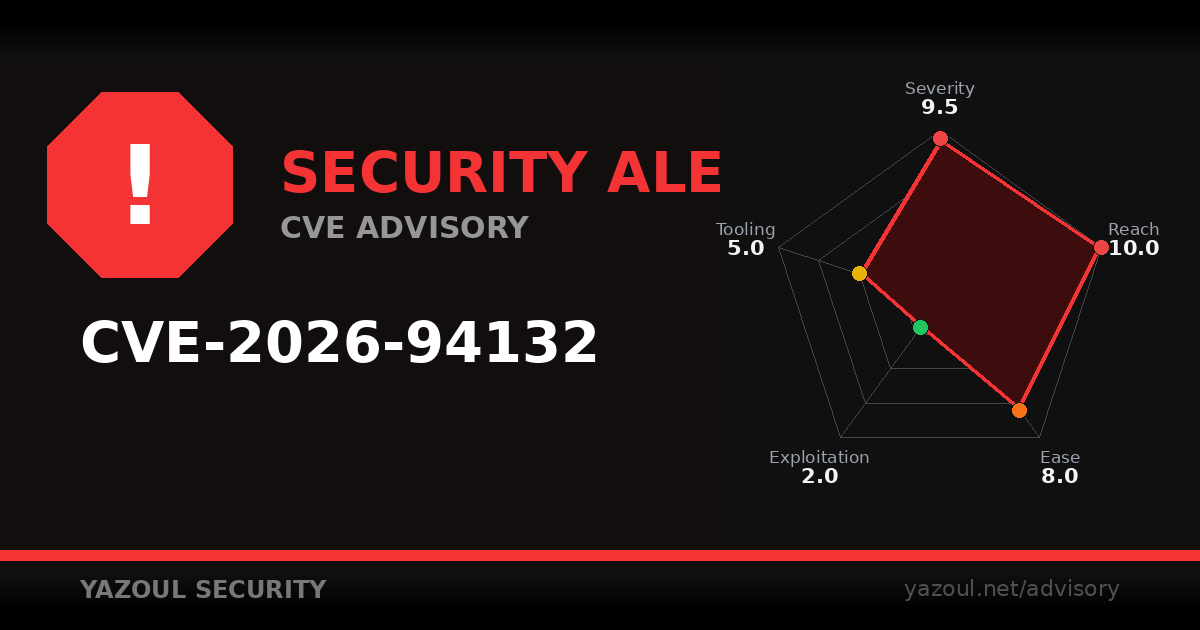
🔴 New security advisory:
CVE-2026-94132 affects multiple systems.
• Impact: Remote code execution or complete system compromise possible
• Risk: Attackers can gain full control of affected systems
• Mitigation: Patch immediately or isolate affected systems
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-94132-acymailing-rce-unauthenticated-email-upload-poc
by Yazoul AI
#CVE #PatchNow #InfoSecCommunity
Two Citrix NetScaler zero-day RCE flaws are under active exploitation. Citrix confirmed CVE-2026-88771 and CVE-2026-88772 and shipped patches. Update now.
#Citrix #NetScaler #ZeroDay #RCE #CyberSecurity #VPN #watchTowr #PatchNow
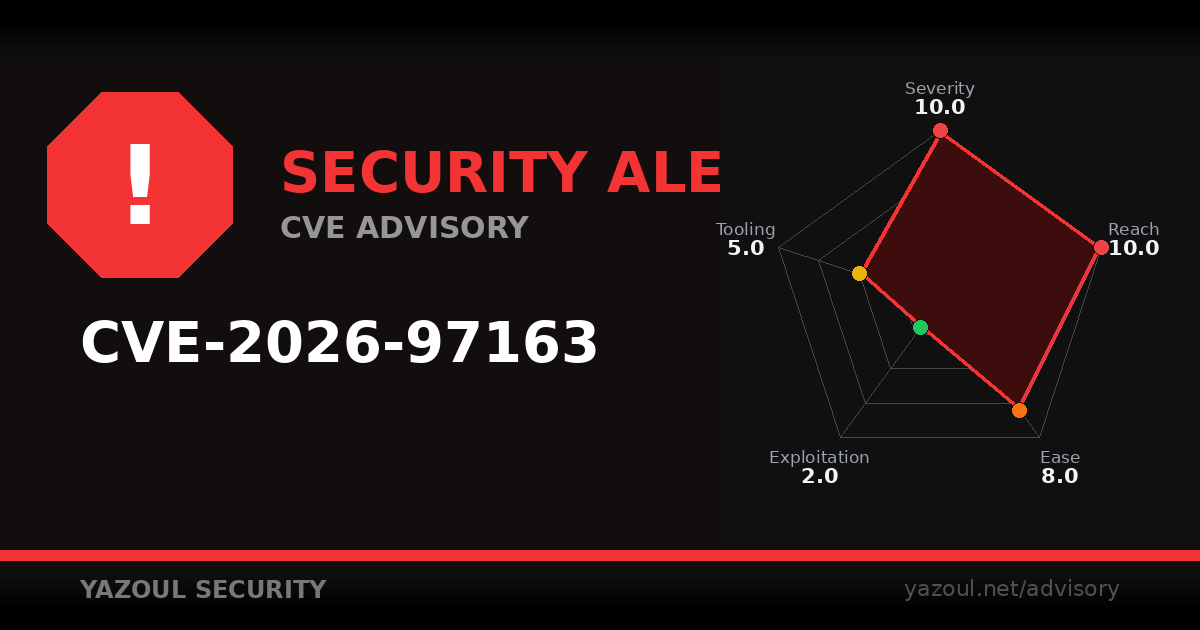
🔴 New security advisory:
CVE-2026-97163 affects multiple systems.
• Impact: Remote code execution or complete system compromise possible
• Risk: Attackers can gain full control of affected systems
• Mitigation: Patch immediately or isolate affected systems
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-97163-joomla-up-plugin-rce-patch-now-poc
by Yazoul AI
#CVE #PatchNow #InfoSecCommunity
🔴 New security advisory:
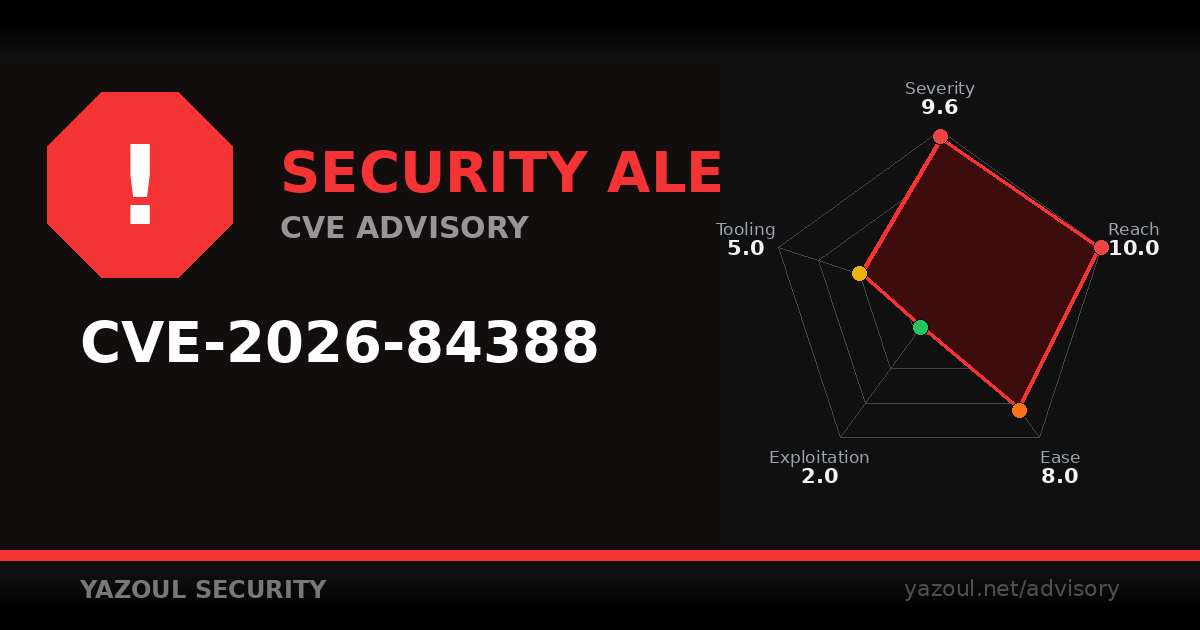
CVE-2026-84388 affects multiple systems.
• Impact: Remote code execution or complete system compromise possible
• Risk: Attackers can gain full control of affected systems
• Mitigation: Patch immediately or isolate affected systems
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-84388-fortipam-chrome-extension-leaks-credentials-poc
by Yazoul AI
#InfoSec #PatchNow #InfoSecCommunity
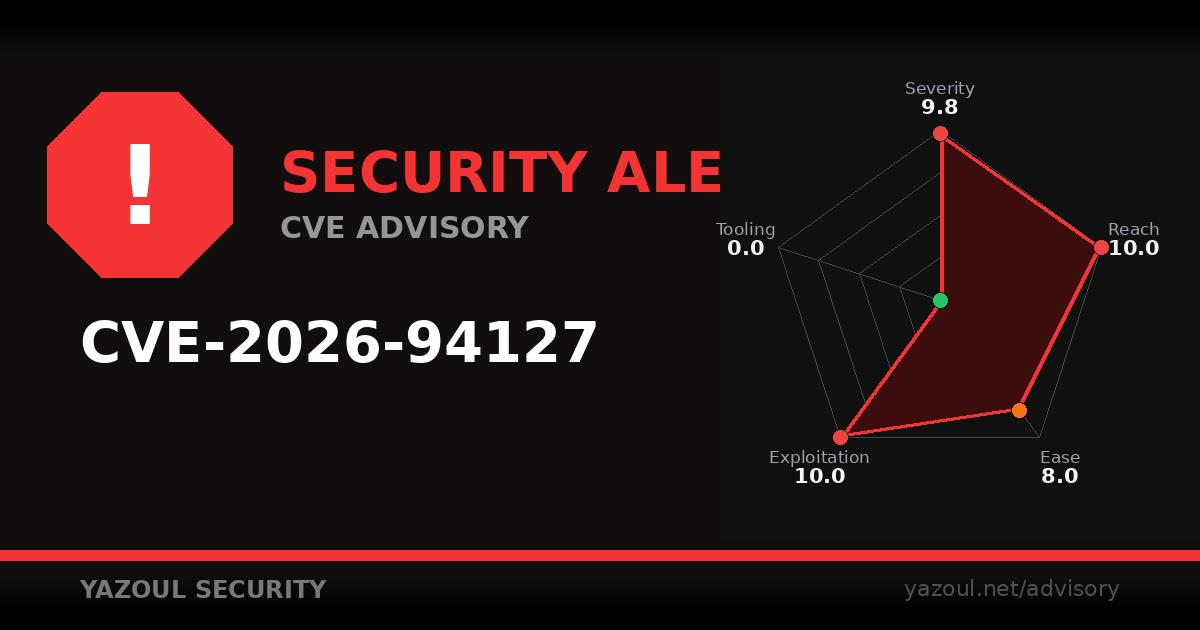
🔴 New security advisory:
CVE-2026-94127 affects multiple systems.
• Impact: Remote code execution or complete system compromise possible
• Risk: Attackers can gain full control of affected systems
• Mitigation: Patch immediately or isolate affected systems
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-94127-big-ip-apm-unauthenticated-rce-exploited-in-the-wild
by Yazoul AI
#InfoSec #PatchNow #InfoSecCommunity
Pega patched a SAML authentication bypass in Pega Platform, rated Critical 9.5 and High 7.0. No CVE, no known compromise. See affected versions and fixes.
#Pega #SAML #AuthenticationBypass #SSO #PegaPlatform #IAM #Vulnerability #PatchNow
Check Point Security Mgmt & Log Server hit by CRITICAL RCE (CVE-2026-91843) via unauthenticated login. No active exploitation yet. Patch ASAP. Tanium (SQLi, RCE) & Kaspersky (Redis) also patched. https://radar.offseq.com/threat/check-point-kaspersky-tanium-patch-product-vulnerabilities-ae8c3757ea9b181a #OffSeq #Vulnerability #RCE #PatchNow
The WordPress 7.1.1 security release fixes 11 flaws, including stored cross-site scripting and path traversal. Update your sites immediately.
#WordPress #WordPress711 #WebSecurity #XSS #CMS #Vulnerability #InfoSec #PatchNow #CyberSecurity #WebDev
Cisco patched 18 Secure Firewall vulnerabilities in FMC, ASA, and FTD, including critical unauthenticated root remote code execution flaws. Update now.
#Cisco #SecureFirewall #FMC #ASA #FTD #CVE #RCE #NetworkSecurity #InfoSec #PatchNow
MongoDB fixed 24 MongoDB Server vulnerabilities, including a critical auth bypass (CVE-2026-82067) and unauthenticated denial of service flaws. Patch now.
#MongoDB #Vulnerability #CVE #DatabaseSecurity #DenialOfService #InfoSec #PatchNow #CyberSecurity #MongoDBServer #AppSec
CVE-2026-59346, a critical VMware Workstation vulnerability, lets an attacker escape a guest VM and execute code on the host. Broadcom rates it 9.3 CVSS.
#VMware #Workstation #Fusion #CVE202659346 #VMXNET3 #Broadcom #InfoSec #PatchNow
This weekly CVE report covers 1,877 new CVEs and 6 actively exploited flaws added to CISA KEV, including N-able, TeamCity, and Langflow bugs.
#CVE #CISAKEV #VulnerabilityManagement #InfoSec #PatchNow #CyberSecurity
A critical Veeam ONE vulnerability, CVE-2026-64633, allows remote unauthenticated code execution at CVSS 10.0. Update to build 13.1.0.7034 now.
#Veeam #VeeamONE #CVE202664633 #RCE #RemoteCodeExecution #Vulnerability #CVSS10 #PatchNow #CyberSecurity #InfoSec
The latest GitLab patch release fixes 13 vulnerabilities, including CVE-2026-6267, a high-severity data exposure flaw. Update self-managed GitLab now.
#GitLab #CVE20266267 #DevSecOps #Vulnerability #PatchNow #InfoSec
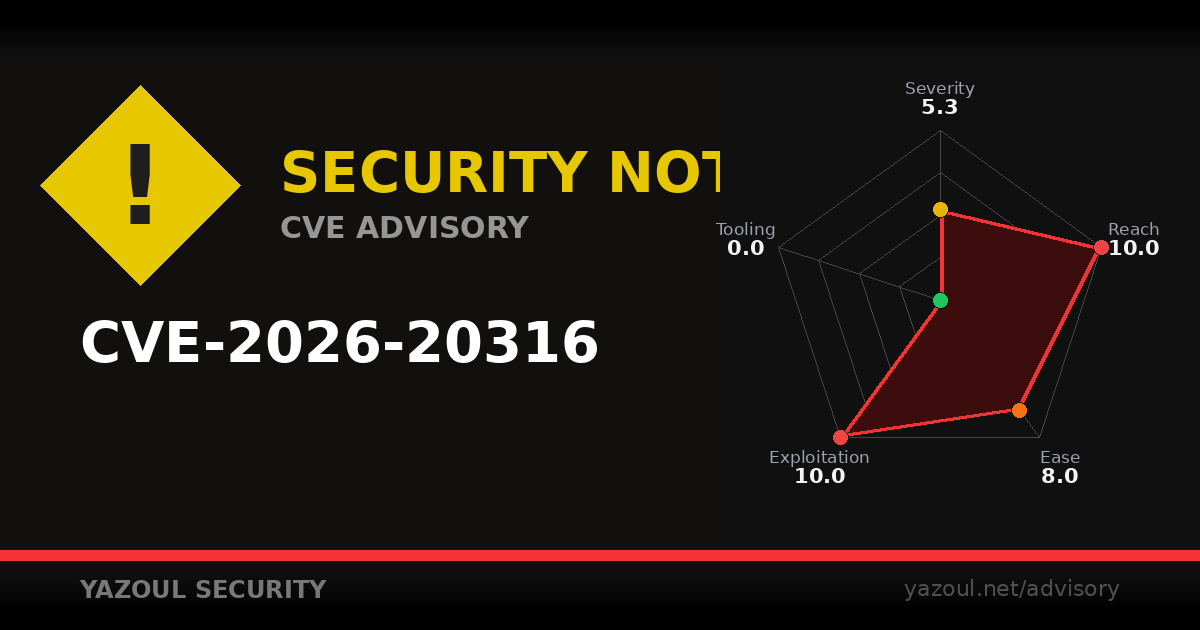
🟡 New security advisory:
CVE-2026-20316 affects Cisco Secure Firewall Management Center.
• Impact: Security weakness that could be exploited
• Risk: Potential for targeted attacks
• Mitigation: Schedule patching in your next maintenance window
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-20316-fmc-static-credentials-leak-sensitive-data
#CVE #PatchNow #InfoSecCommunity
A Konnectivity vulnerability (CVE-2026-16242, CVSS 9.4) lets unauthenticated attackers proxy and modify control-plane traffic. See the fix and mitigation.
#Konnectivity #Kubernetes #CVE202616242 #CloudSecurity #ControlPlane #AuthBypass #InfoSec #PatchNow
Google's Chrome security update fixes four high-severity bugs, including CVE-2026-16807, a Codecs flaw that could enable a sandbox escape. Update now.
#Chrome #ChromeUpdate #SandboxEscape #UseAfterFree #Google #PatchNow
An HTTP/2 DoS vulnerability lets unauthenticated attackers exhaust server memory via stalled flow control. CVE-2026-59762 and CVE-2026-59173 are patched.
#HTTP2 #DoS #DenialOfService #CVE202659762 #CVE202659173 #FlowControl #InfoSec #PatchNow


![AcyMailing RCE, unauthenticated email upload (CVE-2026-94132) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-94132-acymailing-rce-unauthenticated-email-upload-poc.png)

![Joomla UP plugin RCE, patch now (CVE-2026-97163) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-97163-joomla-up-plugin-rce-patch-now-poc.png)
![FortiPAM Chrome Extension leaks credentials (CVE-2026-84388) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-84388-fortipam-chrome-extension-leaks-credentials-poc.png)
![BIG-IP APM unauthenticated RCE exploited in the wild (CVE-2026-94127) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-94127-big-ip-apm-unauthenticated-rce-exploited-in-the-wild.png)