#pentesting
35 posts · Last used 23d
Boosted by @welcome@friends.deko.cloud
Hello, this is EliTechZ.
Infrastructure that performs. Security that holds. Two promises we build everything around.
We are a hands-on technical partner for businesses worldwide: infrastructure, AI integration and security work, from design through deployment, documentation and knowledge transfer.
Visit https://elitechz.com (no analytics, ad pixels or marketing cookies)
Happy to talk cloud, pentesting and incident response here.
#Introduction #CyberSecurity #InfoSec #CloudEngineering #PenTesting #EliTechZ
Replying to
If I don't get any volunteers I'm going to have to wear a hoodie, don a Guy Fawkes mask, and start frantically typing in my basement like the media's version of a hacker.
But seriously, if anyone wants me to identify public vulnerabilities in their systems that attackers could exploit, please DM me. No charge and no shenanigans.
#WhiteHat #PenTesting #PenTest #Hacking #Vulnerability #vulnerabilities
Replying to
“Founded three years ago and based in Tel Aviv, Irregular is a niche player in artificial intelligence, backed with $80 million from Sequoia and #RedpointVentures and valued last year at $450 million. Its technology serves as a sort of #cybersecurity test bed for AI models.
With the leading models becoming ever more powerful, their ability to act in malicious ways is turning into a major threat for corporations and governments, especially as the risk involves hacking into critical computer #systems and #infrastructure. The recent exploits at OpenAI, Anthropic and Meta all involved their AI models accessing websites that should have been off-limits as part of the cybersecurity testing.
#Irregular’s name kept coming up because it was identified as hosting the so-called evaluation testbed.”
Meanwhile #VC money is having a two-way bet; Money on #AI; Money on #hacking AI-models… I mean *cough* #Pentesting *cough*
#PatternLabs / #DanLahav ex IBM / #OmerNevo ex google / #Sequoia #ShaunMaguire #DeanMeyer / #CyberOffensive / #AIModel #AIKillSwitch
CVE triage tip: before exploiting, fingerprint the exact build. Banner grabbing lies—use response behavior. Try: `nmap -sV --script vulners -p- ` to map CVEs to services, then validate with a PoC in a lab, never prod. Practice on bug404found: https://bug404found.com/?utm_source=mastodon&utm_medium=social&utm_campaign=awareness&utm_content=en #cybersec #infosec #security #CVE #Pentesting #VulnerabilityManagement
What Happened to HackerOne?
HackerOne has changed significantly from the bug bounty platform many researchers knew in the late 2010s.
Its current direction is increasingly centered around Hai, AI-assisted triage, vulnerability validation, agentic testing, continuous testing and CTEM.
But the question isn't simply whether HackerOne uses AI. It's how researcher submissions, security intelligence and AI-driven workflows fit together, and what that means for the role and value of human vulnerability researchers.
I dug into HackerOne's history, funding, Live Hacking Events, pricing shift, AI architecture, researcher-data controversy and current product strategy.
https://thecybersecguru.com/analysis/what-happened-to-hackerone/
#HackerOne #BugBounty #InfoSec #CyberSecurity #AppSec #VulnerabilityResearch #AISecurity #CybersecurityResearch #EthicalHacking #Pentesting #AgenticAI #CTEM #SecurityResearch #BugBountyHunters #ApplicationSecurity
Replying to
New blog post!
I recently got to use both of the tools I published on Codeberg (Axmar and Tessera) during an engagement, and so I decided to make a brief writeup as a case study of what these tools can do.
https://ti-kallisti.com/tales/schedule.html
#infosec #pentesting #redteam #redteaming #Microsoft #ActiveDirectory #MSSQL
El lado del mal - Bootcamp de Ciberseguridad Defensiva y Ofensiva en HackBySecurity https://www.elladodelmal.com/2026/07/bootcamp-de-ciberseguridad-defensiva-y.html #BootCamp #Ciberseguridad #Pentest #Pentesting #0xWord #MyPublicInbox #Online
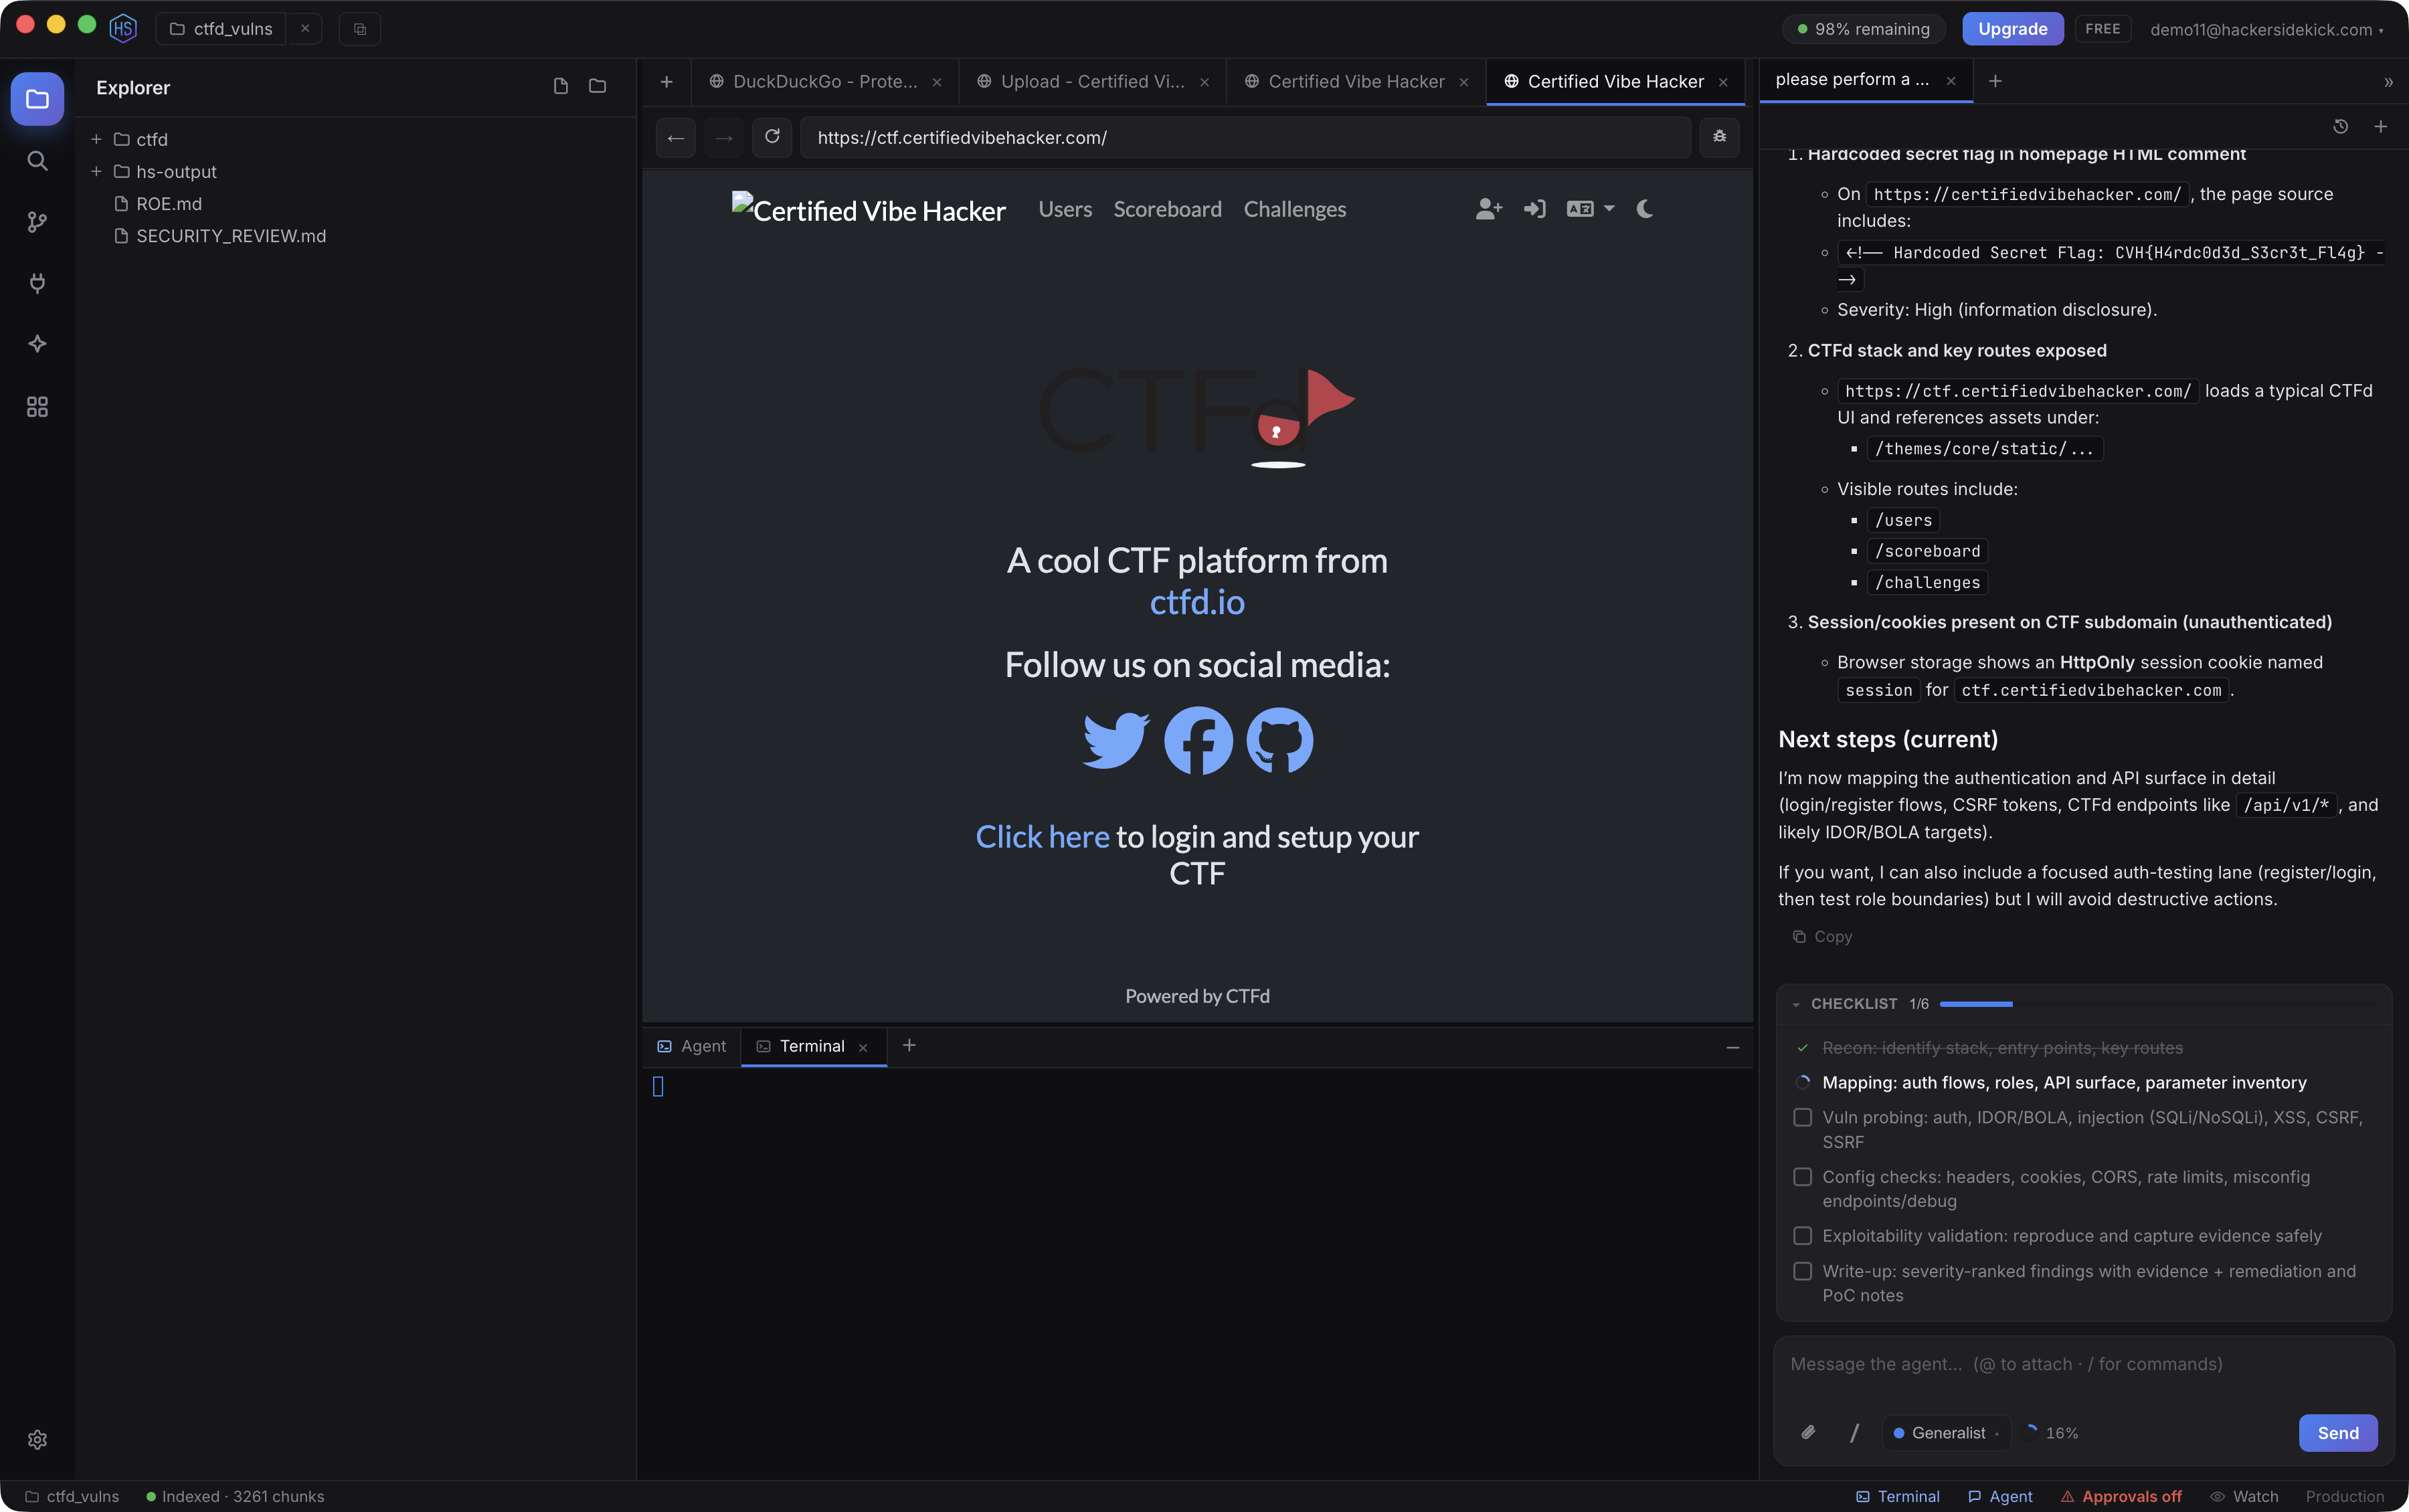
The Agentic Workbench for Cybersecurity has been rebuilt from the ground up. Our biggest update ever!
Hacker Sidekick actually does the work in one window where the analysis lives next to the execution.
What the rebuild unlocks:
An agent that drives a real browser. Not screenshots of a browser, a real sandboxed Chromium it operates for you. It inspects the DOM, pulls full request and response bodies, reads storage and cookies including HttpOnly, walks login flows, and intercepts traffic proxy-style to hold, modify, or block requests.
77 tool integrations that pull your critical data into one place. Threat intel, SIEM, EDR, and ticketing, plus a built-in intel server with MITRE ATT&CK, NVD, VirusTotal, Shodan, Censys, and Exploit-DB out of the box with no key.
Watch mode, a second set of eyes. Toggle it and a passive monitor observes your terminal and browser and surfaces brief advice: a missed step, forgotten cleanup, a scope concern. It only advises. It has no tools of its own and never acts.
Because it is one integrated environment instead of a browser tab bolted onto a chat, all of this is faster, more powerful, and more connected. The agent plans and asks, security modes and approval gates keep it in bounds, and every command it runs is visible. Nothing happens off-screen.
That is the integrated hacking environment. Full tour: https://hackersidekick.com/inside-hacker-sidekick-desktop-feature-tour.html?utm_source=linkedin&utm_medium=social&utm_campaign=desktop_feature_tour
#cybersecurity #infosec #pentesting #hackersidekick #AI #dfir #redteam #threatintelligence
SSH (Secure Shell) - Attacks and Best Practices by Compass Security
- Recon & Info Leakage
- Authentication, CAs, MFA & FIDO2
- Port Forwarding / Tunneling, Agent Forwarding
- Hardening, Post-Quantum Crypto, Auditing & more
SSH (Secure Shell) - Attacks and Best Practices
Your router's admin password might be sitting in a random Reddit comment right now.
I proved it. Captured a WPA2 handshake, cracked it, then found the real admin password buried in a years-old Reddit thread after every official default failed.
Full attack chain from capture, cracking, OSINT, lateral movement to hardening the router against the CISA Project Upskill checklist.
Medium: https://medium.com/radio-hackers/beyond-cracking-the-4-way-handshake-how-i-used-hcxdumptool-hashcat-and-osint-to-compromise-a-62a968cb0611
Hackernoon: https://hackernoon.com/beyond-cracking-the-handshake-a-technical-analysis-of-wpa2-weaknesses-and-router-exposure
#CyberSecurity #WiFi #InfoSec #WPA2 #PenTesting
🤖 Oxjade/rouge-kali: Offensive security skill framework for AI agents (Claude Code, OpenClaw, Hermes Agent). Dual-track analysis: Web/App security + Smart Contract auditing, with configurable depth from surface scan to guardrail-breaking.
🔗 https://github.com/Oxjade/rouge-kali
#CyberSec #InfoSec #AI #Pentesting #OffensiveSecurity
Meet SOMA — an ultra-small (12x13mm) ATmega32U4 USB-HID keystroke injection device designed for physical security assessments and hardware hacking. Protrudes only ~1.5mm from a USB port for a flush, covert footprint.
Fully open-source schematics & firmware:
https://github.com/nebojsa-sjekloca/soma
First batch is now live on Tindie:
https://www.tindie.com/products/42127/
#RedTeam #HardwareHacking #BadUSB #Infosec #OpenSource #Pentesting #Embedded
Sadly it looks like I habe to use ai soon.
any tips on setting up an automated agentic pentester?
I'm running containerized ollama and hermes with an rtx5060Ti passthrough and gemma4-12b.
looking for skills, (uncensored) models, workflows, Plugins etc to run pentests.
also set up parrot os security docket and gave the ai ssh access to it.
#ai #agenticai #hermes #hermesagent #pentesting #penetrationtesting
We kept getting asked the same handful of questions before people would trust us with a scan against prod.
So we answered them properly instead of one at a time on sales calls.
Non-destructive by default. Our own detection engines, not a wrapper around someone else's open source tools. Findings come with evidence, not just a severity label. Data stays on EU infrastructure, workspaces isolated.
Full FAQ: https://pentest-tools.com/product/faq
#offensivesecurity #pentesting
🔴 ServiceNow’s sandbox escape RCE hole now exploited in the wild
📝 A sandbox security hole that could lead to remote code execution (RCE), pat...
https://www.csoonline.com/article/4198993/servicenows-sandbox-escape-rce-hole-now-exploited-in-the-wild.html
📰 CSO Online
#ZeroDay #Pentesting
Browser exploitation isn't web bugs. It's memory corruption across three processes. This issue walks the full chain: V8 JIT type confusion for arbitrary read/write, WebAssembly RWX pages to run shellcode, WebGPU/Dawn as the softer GPU-process target, and the renderer→GPU→broker sandbox escape that ends in --no-sandbox. https://www.kayssel.com/newsletter/issue-59/
#InfoSec #CyberSecurity #Pentesting #BugBounty #BinaryExploitation #WebGPU
🔍 Google fixing Android lock screen bug that lets Gemini send SMS with...
📝 Someone gets ho...
https://www.theregister.com/security/2026/07/17/google-fixing-android-lock-screen-bug-that-lets-gemini-send-sms-without-a-pin/5273027
📰 www.theregister.com - Articles
#CyberSecurity #Pentesting
🍵 HTB Timelapse 🍵
Learn how to:
- Extract PFX certificates for WinRM authentication
- Use LAPS to recover domain administrator passwords
🎬️Watch it here: https://www.youtube.com/watch?v=LlpMSlyzOKg
#HTB #HackTheBox #OSCP #Pentesting #EthicalHacking #Cybersecurity #RedTeam #CTF
HTB Timelapse Walkthrough | OSCP Prep
New blog post!
This time I talk about my new favorite evasive shellcode loader, Charon. I give a brief overview about what it does, how it works and which techniques it uses.
Also a brief addendum for enjoyers of bloated Implants such as Sliver.
https://ti-kallisti.com/general/ms/descending-into-hades.html
#InfoSec #Malware #Shellcode #RedTeam #RedTeaming #Pentesting #Charon #Sliver #Merlin #Mythic
oproxy (open source mitm server) in v0.1.10 released
https://secburg.com/posts/oproxy-v0110-released/
#oproxy #OpenSource #PenTesting #WebSecurity #Proxy #mitm