#2fa

36 posts · Last used 10d

Hi Mastodon. We’re MELKEM™, a small software company in Canada. Our first app is MELKEM Authenticator: two-factor codes for iPhone that stay on the iPhone. No account, no cloud, and the app never connects to the internet. Free, with no ads and no in-app purchases. https://melkem.com/authenticator (Video made with AI.) #introduction #privacy #2FA #iOS #Canada
0
0
1
0
Getting my TOTP data out of Twilio's Authy app thanks to the GDPR: https://blog.tomayac.com/2026/10/17/getting-my-totp-data-out-of-twilios-authy-app-thanks-to-the-gdpr/ New blog post in which I document how I used the sledgehammer 🔨 that is #GDPR to get my #TOTP #2FA 🔐 data out of #Authy and built myself a TOTP Vault PWA.
0
0
0
0

Y’all! Please, please, please use appropriate passwords. We’re seeing a big spam campaign across the fediverse, using hacked accounts.

First, change your fediverse password. Especially if it’s reused elsewhere, short/weak, or really old.

Then, here are some simple steps to protect you and your accounts:

  1. Never reuse passwords. Use a password manager so you’ll only have to remember one password.

  2. Make sure your passwords are secure. They should be 12+ characters with at least one capital letter and one special character. Good password managers have a generator built-in.

  3. Set-up multi-factor authentication (MFA/2FA).

  4. Use passkeys wherever possible.

If you need help, ask someone. Folks who know will help.

#Passwords #Security #InfoSec #OpSec #2FA #MFA #Mastodon #Fediverse #FediTips #MastodonTips

12
1
15
0
Replying to
@markwyner@mas.to : in addition, — At least on Android and iOS/iPadOS devices, configure your OS and password manager to use AutoFill. This helps prevent phishing via fake websites (often using a slightly different domain name, while the login page looks identical to the one on the real website). See the screenshot below (additional details in the Alt text). — Important: when using AutoFill, if no credentials pop up from your password manager, don't start looking in the database itself like Troy Hunt did by mistake (https://www.troyhunt.com/a-sneaky-phish-just-grabbed-my-mailchimp-mailing-list/) — Make a backup of your password manager database after each change. Preferable have multiple backups, at least one offline. — Configure your browser to always warn for http (instead of https) connections. — When using unique strong passwords, don't use weak 2FA/MFA. The advantage is negligeable while the risk of account lockout (caused by loss of the second factor) is huge. In particular TOTP sucks; most "Authenticator" apps are insecure privacy-risky stupid password managers without phishing resistance. More info in https://todon.nl/@ErikvanStraten/115611078608008423 #AutoFill #PasswordManager #StrongPasswords #2FA #MFA #TOTP #WeakMFA #Weak2FA
0
0
0
0
How TOTP Two-Factor Authentication Works Under the Hood: RFC 6238 Mathematics, Dynamic...#totp #2fa #rfc6238 #hotp #software #coding #development #engineering #inclusive #community How TOTP Two-Factor Authentication Works Under the Hood: RFC 6238 Mathematics, Dynamic Truncation, Time Drift Windows, and
0
0
0
0
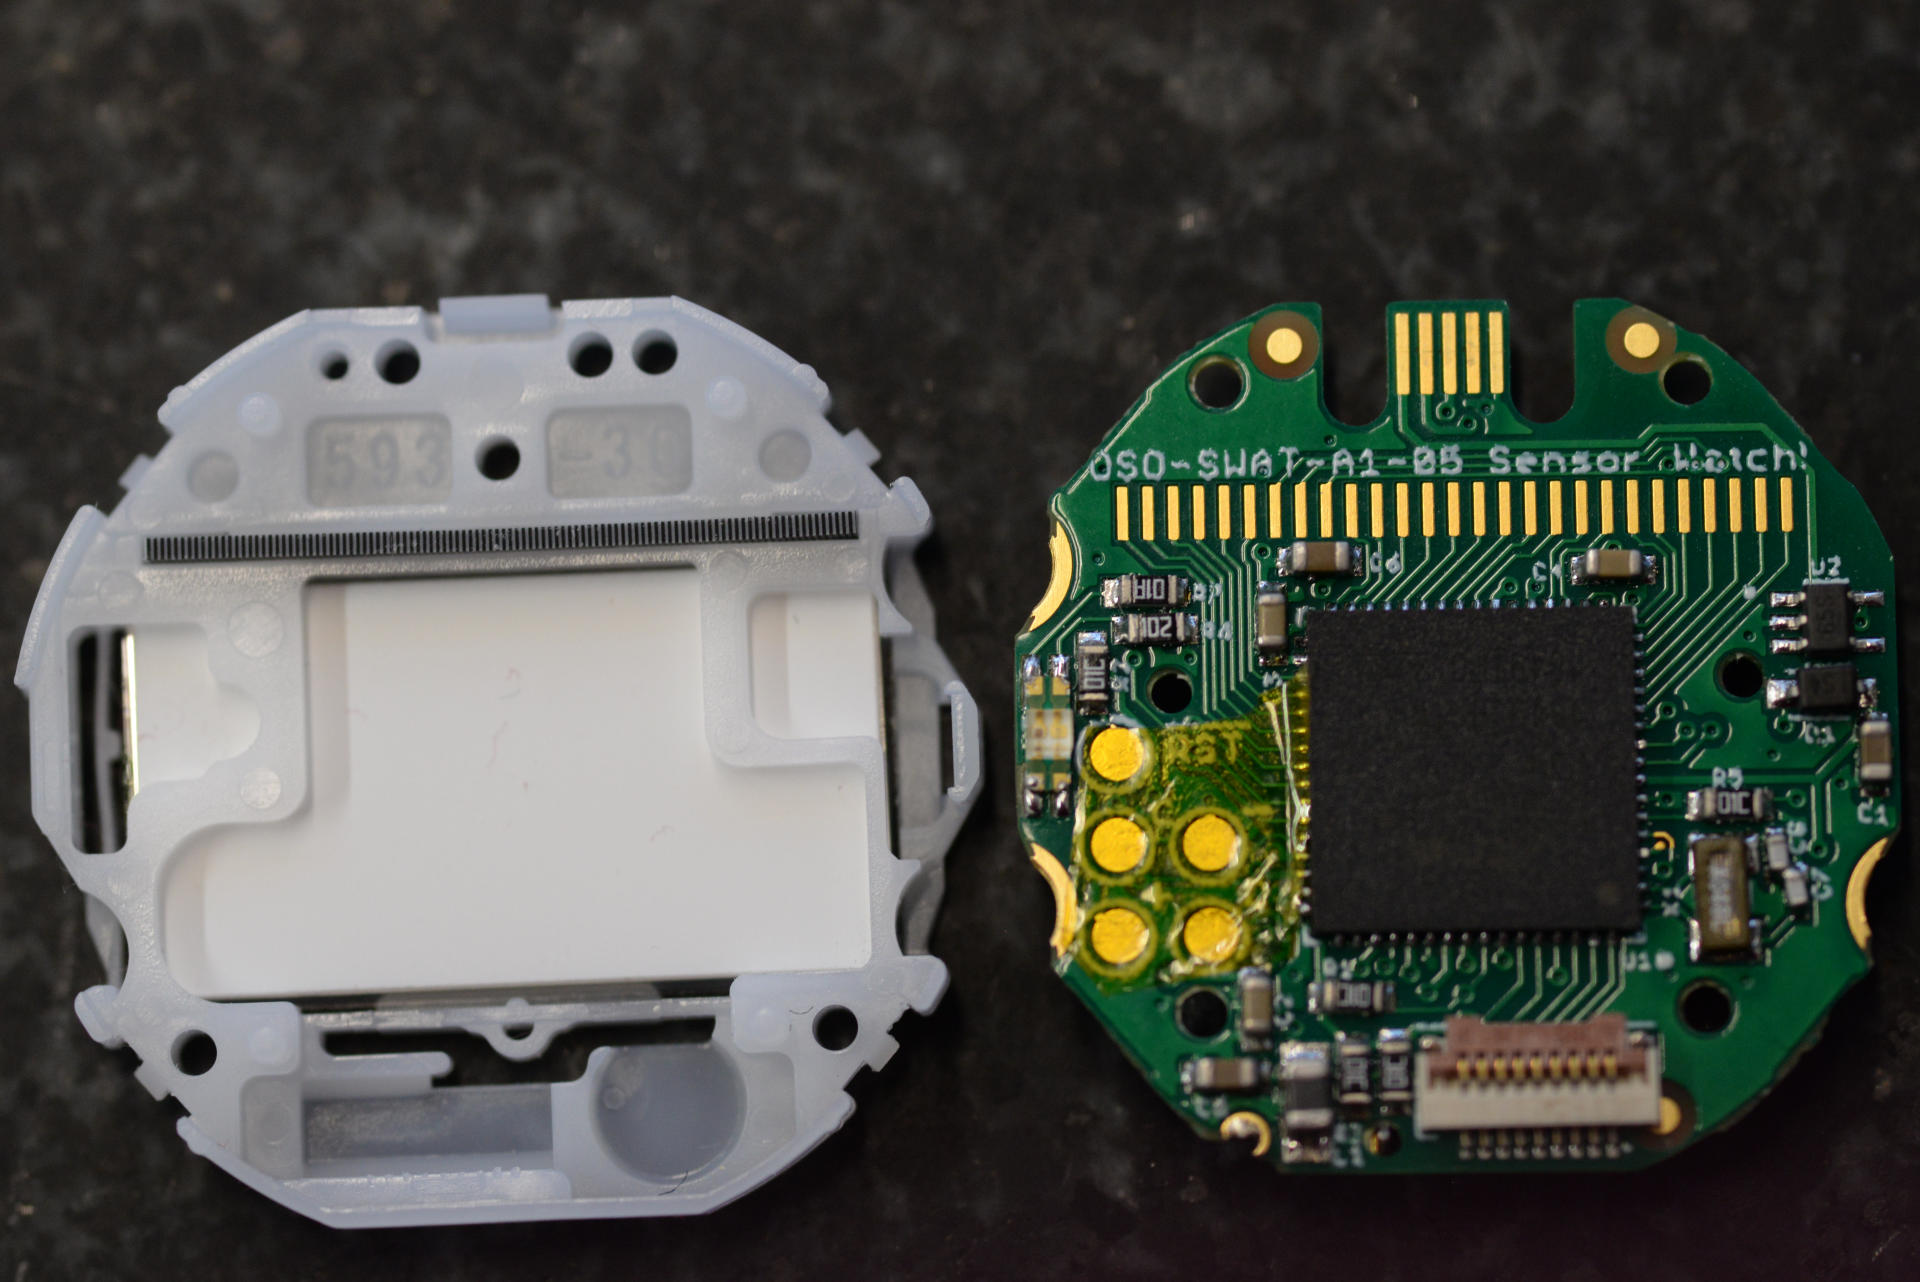
Did I mention, that #SensorWatchPro is pretty cool? With the totp_lfs_face #complication, I now have #TOTP #2FA on my #wristWatch, and it's not even a #smartwatch. https://www.sensorwatch.net/ Thanks, @joeycastillo@mastodon.social! (I use it only for non-critical logins, because access to the secrets is too easy with physical access to the device. E.g. NOT for #salsa #debian org.)
0
0
0
0
Replying to
Not only is Center for Internet Security, Inc. (CIS) still sending these, but they still have no multi-factor authentication for accounts. From https://www.cisecurity.org/about-us The CIS Vision Leading the global community to secure our ever-changing connected world. The CIS Mission Our mission is to make the connected world a safer place by developing, validating, and promoting timely best practice solutions that help people, businesses, and governments protect themselves against pervasive cyber threats. https://www.youtube.com/watch?v=51gf648nRyE&t=118s #Phishing #ComplianceVsSecurity #CIS #CenterForInternetSecurity #MFA #2FA #InfoSec #InformationSecurity #CyberSecurity
1
2
1
0
Replying to
While it may have taken them a moment, with the new CIS Portal for CIS Workbench, they have announced that, "When your account is ready, you'll be guided through a brief process to choose a primary verification method, .." Hardware tokens and/or passkeys, right? "..like SMS ..." When your account is updated, be sure to visit the Portal for "CIS-curated thought leadership and cybersecurity resources to help you put best practices into action" #Phishing #ComplianceVsSecurity #CIS #CenterForInternetSecurity #MFA #2FA #InfoSec #InformationSecurity #CyberSecurity
0
1
0
0
Replying to
@Sheep_Overboard@infosec.exchange https://my.gov.au/en/myaccount/settings/sign-in-settings#/ --- iirc within here is where you can change your #2FA arrangement, including to #TOTP this is what i see now each time i login; it's really cool & works well NB: you can use KPXC independent of your browser, but best optimisation arises when using it with the official KPXC addon in one's browser, as i learned to do.
2
2
2
0

I noticed that signing in to Mastodon using 2FA didn't reliably work. Turns out my system clock was ~30 seconds behind that of the actual time (currently GMT +1 for me).

On Linux distributions that have systemd, systemd apparently synchronises your system time with a time server automatically. However, I use Devuan (i.e. Debian but without systemd) so I had to do it manually.

I used htpdate to set the time to a UK time server on pool.ntp.org like this:

sudo htpdate uk.pool.ntp.org

No need to reboot. It's now accurate to GMT+1 to within about half a second. :)

Hashtags: #Devuan #time #system #Linux #2FA #systemd #Debian

0
0
0
0
my: bankcredit card ex company1credit card ex company2superannuationmobile phone vendornbn broadband vendor do not use / support #2FA via #MFA #TOTP, & i am tearing my hair out in exasperation at these damn troglodytes. I've even just wasted a coupla hours dealing with my mobile phone vendor who overnight sent out an email that delighted me as it recommended customers setting up our online accounts with them using [direct quote from the fucken email]... MFA is a security method that requires you to prove your identity in two or more different ways, like an additional verification step as part of your login. This might include facial recognition, a dedicated authenticator app, or a unique code sent to your preferred contact method. ...only to eventually find that part of the email is bullshit. jfc, most of these are major companies, some indeed are multi-nationals, yet they still treat security as a joke. utter fuckheads! aaaaaaand yet seemingly not a week goes by without companies getting hacked & thus fucking over their customers 😡🖕
0
0
0
0
Replying to
@Mae@is.badat.dev so can I finally mandate PGP-based 2FA (like on dread)? Cuz I won't install a garbage app that won't run on my devices anyway and I won't have TOTP / HOTP available all the time… #PGO #2FA #App #Enshittification #OTP #TOTP #HOTP
1
2
2
0
Die neue #TOTP Funktion in #ruccuDB 0.0.3 wirkt für eine Daten Engine auf den ersten Blick vielleicht ungewöhnlich. Gerade darin liegt aber ihr Vorteil: TOTP Secrets werden nahtlos in der Engine verwaltet und verschlüsselt gespeichert. Anwendungen, Plugins oder andere Konsumenten können dadurch ohne eigene Kryptografie eine #2fa Lösung auf Basis von RuccuDB in PHP integrieren. #dev #coding #development
0
0
0
0
Replying to
CVE-2025-0679 named them. NVD and MITRE still can't agree on whether you had a fighting chance. You did not. Update your Zimbra webmail client to the patched version immediately, or TA488 keeps the loot. Reward: You've received a hollow Authenticator Token — pre-drained. #ZeroDay #Zimbra #Espionage #CyberSecurity #2FA #AchievementUnlocked (2/2)
0
0
0
0